What needed solving.
Let teams use local provider subscriptions and project tools through a shared company workspace without distributing shared credentials or letting agent work silently publish changes.
- 01Company-scoped request
- 02Enrolled host or sandbox
- 03Artifact + exact-diff approval
Simplified from the implementation and project notes.
How it fits together.
A request stays inside the employee's authority
The web control plane resolves the employee, organization, project and selected agent before dispatch. A connected desktop maintains an authenticated outbound tunnel; the worker routes the request to that enrolled host, where the local T3 runtime uses the host's own provider login, checkout and tools. Hosted E2B runs are a separate option. A consequential design choice is keeping provider credentials on the execution host while applying employee and source permissions again at the company gateway. Tests cover denied tool grants, project/conversation isolation, OAuth token binding and revocation; changed permissions must stop a call even when a conversation or token already exists.
An approval binds to bytes and context
Local edits are submitted as full file contents with a base SHA. The gateway computes and stores the authoritative diff; the approval is tied to that proposal and publishing creates a draft PR only after live authorization succeeds. The decision receipt can be read later without repeating the write. The hash boundary avoids approving a moving target; tests exercise changed action arguments, expired approval, changed agent version and revoked group membership. PR publication does not merge or deploy.
Artifacts use their own origin and sharing rules
Saved HTML is durable object storage content. Private artifact access checks organization membership, while an explicit public link can be revoked; rendering uses an isolated artifact origin that denies application-cookie access and network requests. Artifact sharing is deliberately independent of host and conversation access. Browser acceptance covered generated artifact links and anonymous download rejection; backend-focused tests include SSRF and bounded-body/output validation. These checks establish the documented pilot paths, not every managed connector or external write.
Inside the software.
A team control plane around the pinned T3 Code workbench: local and hosted execution, organization-scoped tools, reviewable writes, and durable outputs. The complete stable T3 web and desktop clients are integrated; some company adapters are configured while others retain explicit capability limits.
Integrated T3 Code workbench
The hosted workbench and separate Linux desktop provide coding and co-working conversations, projects, agents, and provider settings using pinned upstream T3 Code v0.1.5.
Pinned upstream client/runtime; MWL patches and source boundary recorded in workbench metadata. Desktop uses a separate app identity, data directory, ports, and updater configuration.
Present in the reviewed source.
Implementation references
morewithless/README.mdmorewithless/docs/t3-foundation-plan.mdmorewithless/workbench/MOREWITHLESS-UPSTREAM.jsonmorewithless/workbench/apps/web/src/routes/_chat.tsxmorewithless/workbench/apps/desktop/src
Enrolled desktop execution
An online enrolled computer can run a web-started prompt with its local provider login, checkout, and tools; a browser pairing approval enrolls a new installation.
Worker maintains authenticated outbound HTTP/WebSocket desktop tunnels; employee-scoped authorization is attached to host calls, while provider credentials stay on the host.
Present in the reviewed source.
Implementation references
morewithless/README.mdmorewithless/services/desktop-relay.tsmorewithless/lib/desktop/api.tsmorewithless/tests/backend-desktop.test.ts
Organization, people, groups, and projects
Admins organize work into projects and groups, assign people, and set project/agent defaults that affect new conversations while existing conversation permissions remain fixed.
Better Auth organization membership and server-side authorization; group membership, project membership, source permissions, and agent ceilings are checked on company calls.
Present in the reviewed source.
Implementation references
morewithless/README.mdmorewithless/app/admin/page.tsxmorewithless/components/workspace.tsxmorewithless/lib/access.tsmorewithless/tests/backend-access.test.tsmorewithless/tests/backend-invitations.test.ts
Organization agents and shared skills
Admins define reusable agent instructions, attach shared skills, and set groups and connector capabilities to constrain which members can use each agent.
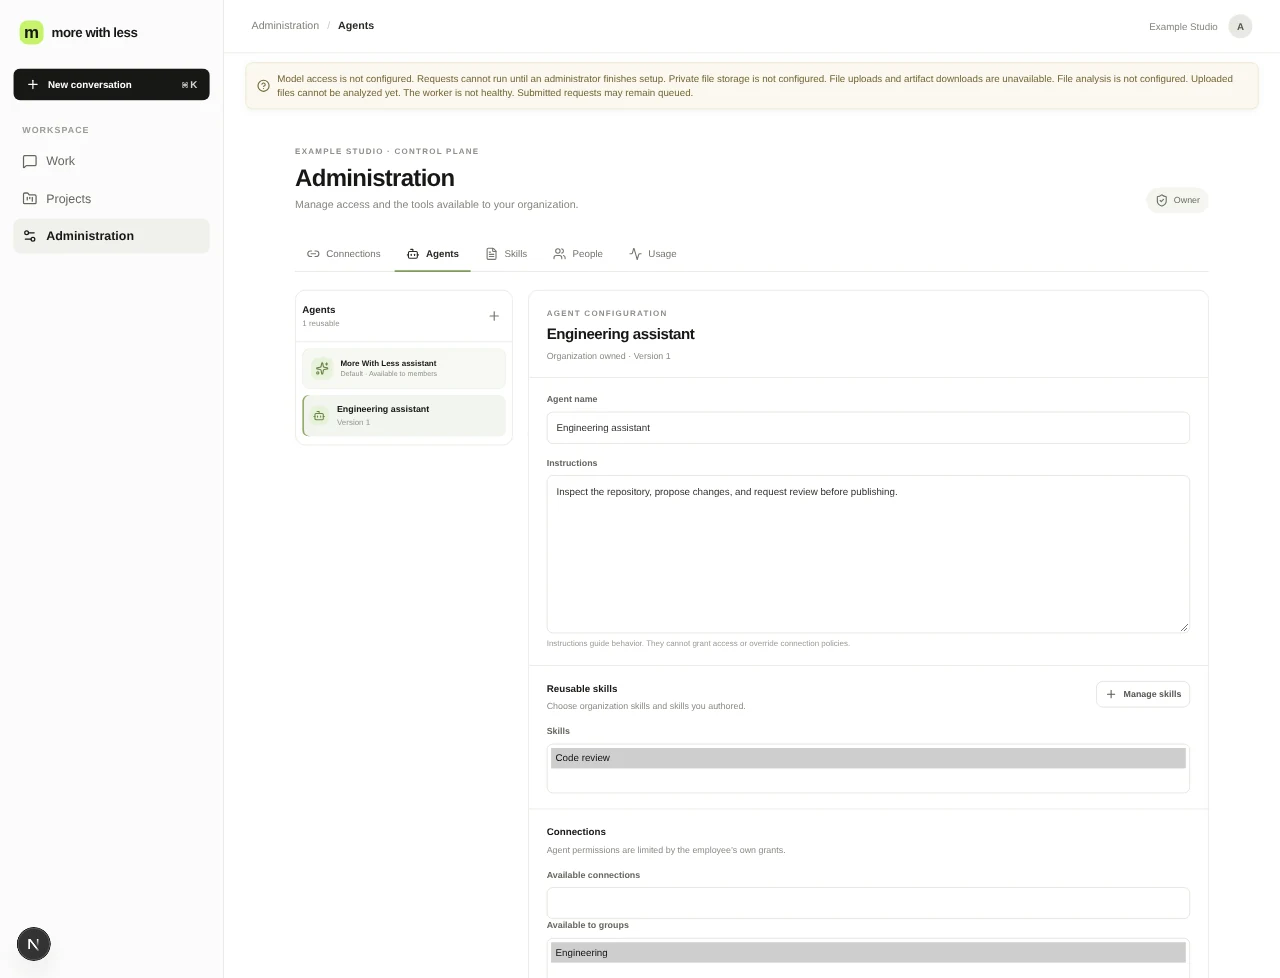
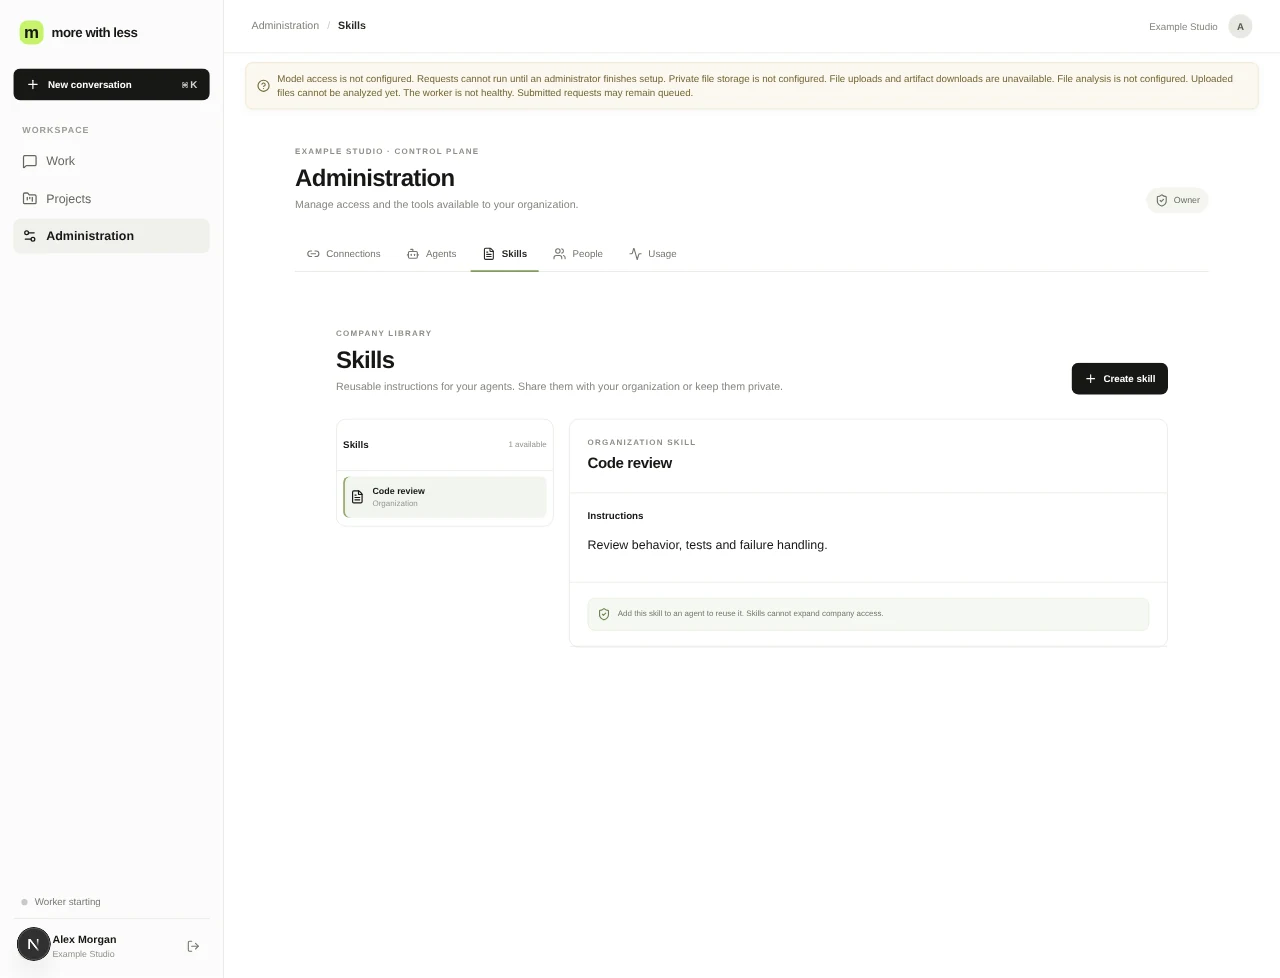
Agents reference skill and connector IDs; actor, group, agent, and source ceilings intersect in authorization. This is a control-plane feature rather than an autonomous monitoring system.
UI captured locally. Data and integration limits are noted above.
Implementation references
morewithless/README.mdmorewithless/components/workspace.tsxmorewithless/lib/contracts.tsmorewithless/tests/backend-company.test.tsmorewithless/tests/runtime-authorization.test.ts
Scoped company connectors
Company connectors expose approved tools to eligible employees while keeping shared integration credentials on the server; new tool discoveries remain blocked until saved explicitly.
Encrypted credentials, discovered tool policies, group scope, per-call membership checks, source auth, and live revocation. Storage Levers is enabled for configured facilities; Metro capability is limited to equipment reads in the documented configuration.
Present in the reviewed source.
Implementation references
morewithless/docs/company-connections.mdmorewithless/README.mdmorewithless/components/company-connections.tsxmorewithless/app/api/company-connections/[[...path]]/route.tsmorewithless/tests/backend-connected-auth.test.tsmorewithless/tests/runtime-security.test.ts
Hosted isolated analysis and previews
Hosted execution can allocate temporary E2B workspaces for repository tasks and serve private previews through workspace-specific origins.
Worker-backed E2B template, bounded run lifecycle, private preview proxy, isolated workspace origin; deployment credentials stay outside E2B.
Present in the reviewed source.
Implementation references
morewithless/README.mdmorewithless/docs/engineering-connections.mdmorewithless/services/engineering-preview.tsmorewithless/Dockerfile.workermorewithless/tests/managed-engineering.test.ts
Exact-diff approval and publication
A proposed local changeset carries its immutable base revision and full content; reviewers inspect the recorded diff and approve the exact proposal before draft PR publication.
Gateway records authoritative diff and approval/version/hash/expiry; decision is consumed once and checked against current permission. Approval does not merge or deploy.
Present in the reviewed source.
Implementation references
morewithless/README.mdmorewithless/docs/engineering-connections.mdmorewithless/lib/desktop/threads.tsmorewithless/app/api/engineering/[[...path]]/route.tsmorewithless/tests/managed-engineering.test.ts
Private artifacts and revocable sharing
Agents save durable HTML artifacts that authorized members can preview or download; public links are an explicit, revocable sharing choice on an isolated origin.
S3 object storage, authenticated artifact APIs, member checks, and restrictive isolated artifact origin that blocks application-cookie access and outbound network requests.
Present in the reviewed source.
Implementation references
morewithless/README.mdmorewithless/components/foundation/share-page.tsxmorewithless/components/foundation/share-management.tsxmorewithless/app/api/shared-artifacts/[id]/route.tsmorewithless/tests/runtime-security.test.ts
Building and checking it.
An employee enrolls a desktop and approves it in the browser. Web prompts can run on that desktop using its local provider login, checkout and tools; alternatively hosted execution is available. Team defaults apply to new conversations.
Reviewers can inspect an output, approve or reject a proposed PR, and read the receipt without repeating the write.
The project documentation states sharing an artifact does not grant access to a host or conversation. Approved PR publication does not merge or deploy customer software. Storage Levers managed data access is enabled only for configured, verified connections.
Source notes
Based on repository code and project records reviewed on October 30, 2026. Historical checks are described as recorded, not rerun for this article. Screenshots, renders, and mockups are labeled individually.
morewithless/README.mdmorewithless/docs/t3-foundation-plan.mdmorewithless/docs/company-connections.mdmorewithless/package.jsonmorewithless/docs/verification-2026-10-29.mdmorewithless/docs/implementation-contract.mdmorewithless/tests/backend-desktop.test.tsmorewithless/tests/runtime-authorization.test.tsmorewithless/tests/runtime-security.test.ts